Cloud Security Checklist India: Before and After Migration
Cloud migration does not transfer every security responsibility to the provider. This cloud security checklist covers the decisions to make before migration and the ongoing checks needed afterwards, including access control, MFA, logging, backups and incident response.
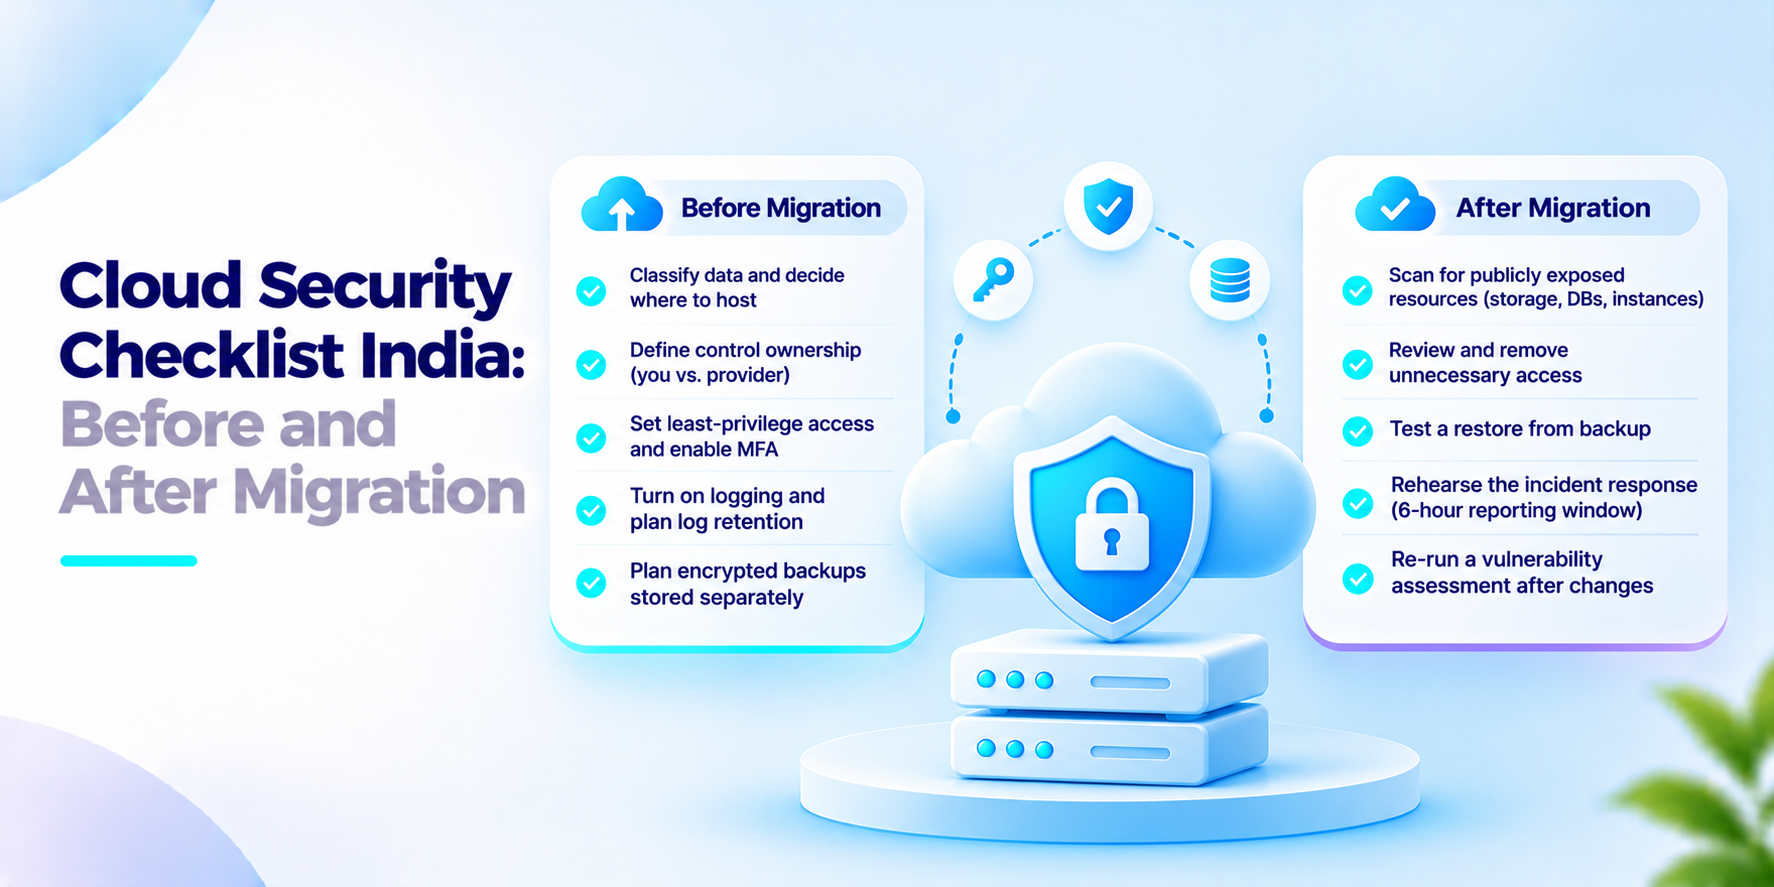
Moving workloads to the cloud does not hand over responsibility. A cloud security checklist in India should cover decisions made before migration and checks that continue afterwards. Most teams finish the part and then drift on the second.
What the India rules say
CERT‑In, India’s national cyber security agency, issued Guidelines on Information Security Practices for Government Entities. Section 9 says cloud services follow a shared responsibility model for security and compliance. It asks organisations to check the accessibility of all cloud instances, apply least privilege with granular permissions, enable cloud‑native security controls with logging for critical resources and require multi‑factor authentication for user accounts. Elsewhere it asks for audits at least every six months, third‑party audits at least yearly, backups kept physically separate from the server and reporting of cyber incidents to CERT‑In within six hours of noticing them.
Three cautions. The guidelines are written for government entities so check whether they apply to your company through contracts or sector rules. The copy reviewed carries no date. And they are principles, not a checklist so they need translating into your own controls.
A cloud security checklist India: before migration
This section is our view. Settle these items before the workload moves.
- Classify the data and decide where each class may be hosted.
- Write down who owns which control under the shared responsibility model, provider or you.
- Create roles with least‑privilege access and turn on multi‑factor authentication for every account.
- Turn on logging and decide how to keep logs and who reads them.
- Plan encrypted backups stored apart from the production environment.
After migration: keep the cloud security checklist India running
Cloud environments change weekly so a checklist done once goes stale. Each month, scan for storage, databases and instances exposed to the internet. Review who holds access and remove accounts that are no longer needed. Test a restore from backup, not the backup job. Rehearse your incident path so you can meet a six‑hour reporting window. Re‑run a vulnerability assessment after changes.
What to ask before you finalise a cloud security checklist in India
- Which controls does the provider handle and which are ours?
- Who is alerted when a resource becomes publicly accessible?
- How quickly can you show the access history for a given account?
- When did you last restore from backup. How long did it take?
- Which regulator, customer contract or sector rule applies to this data?
- Who signs off the cloud security checklist in India after each major change?
How We Approach a Cloud Security Checklist in India
Our Cloud Services cover cloud strategy and consulting, migration, cloud security, DevOps and automation, backup and disaster recovery and monitoring and reporting on AWS, Azure and GCP. We start by agreeing with you what runs where and who owns each control, then turn that into a cloud security checklist for India your team can run after we hand over.
If your team is building a cloud security checklist in India, we would welcome the conversation.
Frequently asked questions
What should a cloud security checklist include before migration?+
It should cover data classification, workload placement, shared responsibility, identity and access management, MFA, logging, encryption, backup planning, network exposure and incident response.
What should organisations check after cloud migration?+
Review public access configurations, user permissions, security alerts, logs, vulnerabilities, backup integrity and incident response readiness. Repeat checks when infrastructure or access configurations change.
What is the shared responsibility model in cloud security?+
It defines which security controls are managed by the cloud provider and which remain the customer's responsibility. The exact division varies by provider and service model, such as IaaS, PaaS and SaaS.
Does CERT-In require cyber incidents to be reported within six hours?+
CERT-In's Directions dated 28 April 2022 require specified cyber incidents to be reported within six hours of noticing them or being informed about them. The requirement applies to the entities covered by the Directions, including service providers, intermediaries, data centres, body corporates and government organisations.
How long should organisations retain cloud security logs in India?+
The CERT-In Directions require covered entities to securely maintain logs of their ICT systems for a rolling period of 180 days within Indian jurisdiction. Organisations should check how this requirement applies to their systems and cloud service arrangements.
Plan Your Cloud Migration with Security in Mind
Get support with cloud strategy, migration, security, backup and monitoring across AWS, Azure and Google Cloud.